Blog

AI in GRC software: 12 questions to ask your vendor

Gaute Wangen

An AI chip, a person who approves and a protected register, connected along a line

Is your GRC vendor adding AI? 12 security and privacy questions to ask about your data, model training, access rights and human review, with good answers.

Is your GRC vendor adding AI? 12 security and privacy questions to ask about your data, model training, access rights and human review, with good answers.

See Full Text

Norwegian Digital Security Act course (DSiP)

Gaute Wangen

Four course sessions shown as steps on a line, with icons for governance, risk, responsibility and preparedness

A four-session course, January to May 2027, where you work through the Norwegian Digital Security Act, NIS2 and DORA in your own organisation.

A four-session course, January to May 2027, where you work through the Norwegian Digital Security Act, NIS2 and DORA in your own organisation.

See Full Text

Records of processing activities: guide and free template

Gaute Wangen

Records of processing activities shown as a table with icons for purpose, data subjects, storage, retention and security

Records of processing (ROPA): GDPR Article 30 requirements, who must keep them, a worked example and a free Excel template you can use straight away.

Records of processing (ROPA): GDPR Article 30 requirements, who must keep them, a worked example and a free Excel template you can use straight away.

See Full Text

Risk and vulnerability analysis in 7 steps, with template

Gaute Wangen

Risk and vulnerability analysis: checklist, risk matrix and the steps of the process

How to do a risk and vulnerability analysis in seven steps: scope, unwanted events, likelihood, impact and measures. With an example and a free template.

How to do a risk and vulnerability analysis in seven steps: scope, unwanted events, likelihood, impact and measures. With an example and a free template.

See Full Text

What is GRC? Governance, risk and compliance explained

Gaute Wangen

Governance, risk and compliance shown as three connected areas

What is GRC? Learn how governance, risk and compliance help organisations make informed decisions, manage uncertainty and meet their obligations.

What is GRC? Learn how governance, risk and compliance help organisations make informed decisions, manage uncertainty and meet their obligations.

See Full Text

What else stops? Understanding IT system and supplier dependencies

Gaute Wangen

Dependency map showing which systems stop or run with reduced function when payroll goes down

Dependency analysis shows what really stops when an IT system or supplier fails, revealing hidden dependencies and single points of failure.

Dependency analysis shows what really stops when an IT system or supplier fails, revealing hidden dependencies and single points of failure.

See Full Text

Norway's Digital Security Act: 7 requirements to meet

Gaute Wangen

The seven key areas of Norway's Digital Security Act (infographic in Norwegian)

Norway's Digital Security Act and regulation in seven practical areas: scope, governance, risk assessment, controls, suppliers, incidents and reporting.

Norway's Digital Security Act and regulation in seven practical areas: scope, governance, risk assessment, controls, suppliers, incidents and reporting.

See Full Text

IT security for small businesses in Norway: 10 answers

Gaute Wangen

Three colleagues at a laptop, surrounded by icons for security measures

Where should a small business in Norway start with IT security and GDPR? Practical answers to the ten most common questions, with a simple checklist.

Where should a small business in Norway start with IT security and GDPR? Practical answers to the ten most common questions, with a simple checklist.

See Full Text

Bowtie Analysis: A Step-by-Step Guide with Example

Gaute Wangen

Bowtie model with causes and control barriers before an unwanted event, and consequences and defence barriers after it

Bowtie analysis maps the causes, consequences and barriers of one unwanted event. A step-by-step guide to bow-tie risk assessment, with a cyber example.

Bowtie analysis maps the causes, consequences and barriers of one unwanted event. A step-by-step guide to bow-tie risk assessment, with a cyber example.

See Full Text

Cybersecurity terminologies

Gaute Wangen

Cover image asking: ICT security, cyber security or information security?

Information security, ICT security, cybersecurity or digital security? We explain how the terms differ and how they relate to each other.

Information security, ICT security, cybersecurity or digital security? We explain how the terms differ and how they relate to each other.

See Full Text

Compliance success

Grethe Østby

Future Ready customer story: from conversation data to ISO/IEC 27001 and ISO/IEC 27701 certification

How Future Ready moved compliance out of spreadsheets and into one system, giving the whole team a shared view of risks, processing activities and tasks.

How Future Ready moved compliance out of spreadsheets and into one system, giving the whole team a shared view of risks, processing activities and tasks.

See Full Text

Training and awareness

Grethe Østby

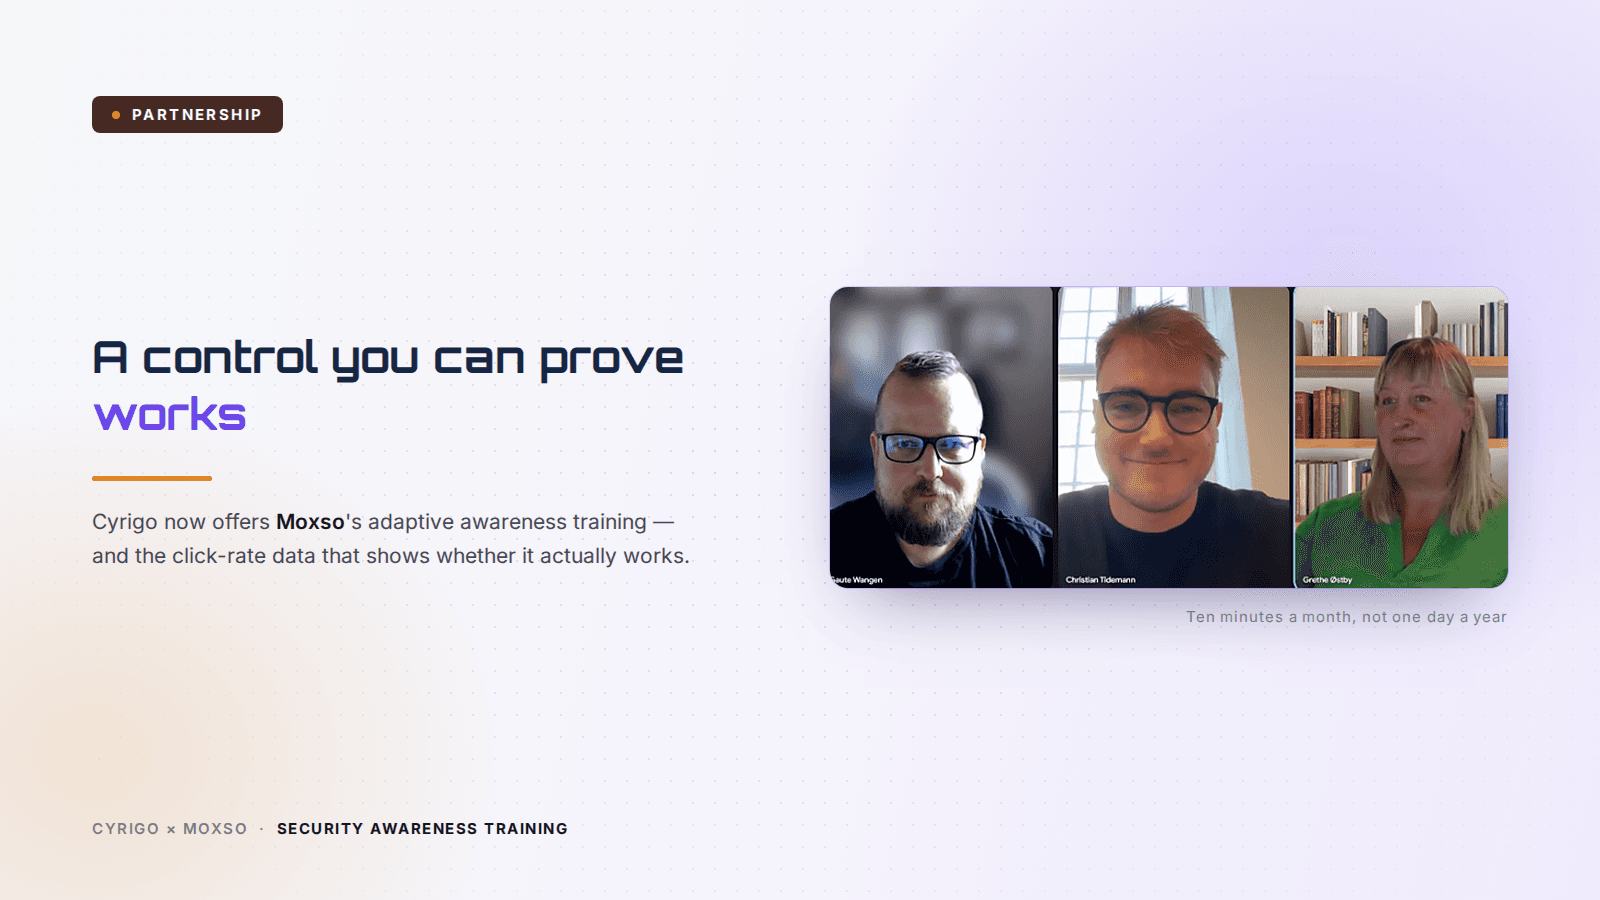
Video meeting about the Cyrigo and Moxso partnership on security awareness training

Cyrigo now offers Moxso’s security awareness training: about ten minutes a month per employee, with short videos, exercises and phishing simulations.

Cyrigo now offers Moxso’s security awareness training: about ten minutes a month per employee, with short videos, exercises and phishing simulations.

See Full Text

Cyrigo logo

Cyrigo stands for cyber risk governance. We are a SaaS built for governance, risk management and compliance.

© 2026 Cyrigo AS. All rights reserved.

Cyrigo logo

Cyrigo stands for cyber risk governance. We are a SaaS built for governance, risk management and compliance.

© 2026 Cyrigo AS. All rights reserved.

Cyrigo logo

Cyrigo stands for cyber risk governance. We are a SaaS built for governance, risk management and compliance.

© 2026 Cyrigo AS. All rights reserved.